

Deprecated Aztec infrastructure has suffered a second exploit within days, adding to concerns about the security of abandoned smart contract infrastructure.
Aztec’s private rollup bridge was exploited on Thursday for 1,158 Ether (ETH), 150,000 Dai (DAI) and 0.46 renBTC (RENBTC), totaling about $2.15 million, according to Cos, the co-founder of cybersecurity company SlowMist.
His preliminary analysis found that the attacker used a false rollup proof to trick the protocol into releasing assets from its reserves to the attacker’s address.
Aztec Labs confirmed the exploit, adding that about $2 million was transferred from an immutable smart contract of a payment product deprecated in 2022, for which Aztec Labs held no admin keys or ability to pause transactions.
Aztec Labs said the incident is separate from the $2.1 million stolen from Aztec Connect’s smart contract on Sunday. Aztec Connect was a privacy-focused rollup that was deprecated in March 2023, with the team halting deposits and shifting resources to the next-generation Aztec Network.
Cointelegraph reached out to Aztec Labs for additional details about the vulnerability but had not received a response by publication.
Etherscan record of the Thursday exploit transaction. Source: Etherscan
Related: AI models led to a ‘vulnerability apocalypse’ in crypto security: Immunefi CEO
Old smart contracts raise new security concerns
The two Aztec exploits, along with the $1.3 million stolen from decentralized exchange Raydium earlier in June, renewed concerns about deprecated smart contracts, as the three incidents stemmed from vulnerabilities in abandoned infrastructure.
“Old contracts continue to be bug bounties available to any hackers. With protocols removing their responsibility to maintain them, they can become even more tempting,” wrote risk analysis platform Blockful in a Tuesday X post.
Despite Aztec Connect being deprecated, the attacker extracted over $2.1 million in the initial exploit as the immutable contract was still holding legacy user assets, wrote SlowMist in a post-mortem analysis of the incident.
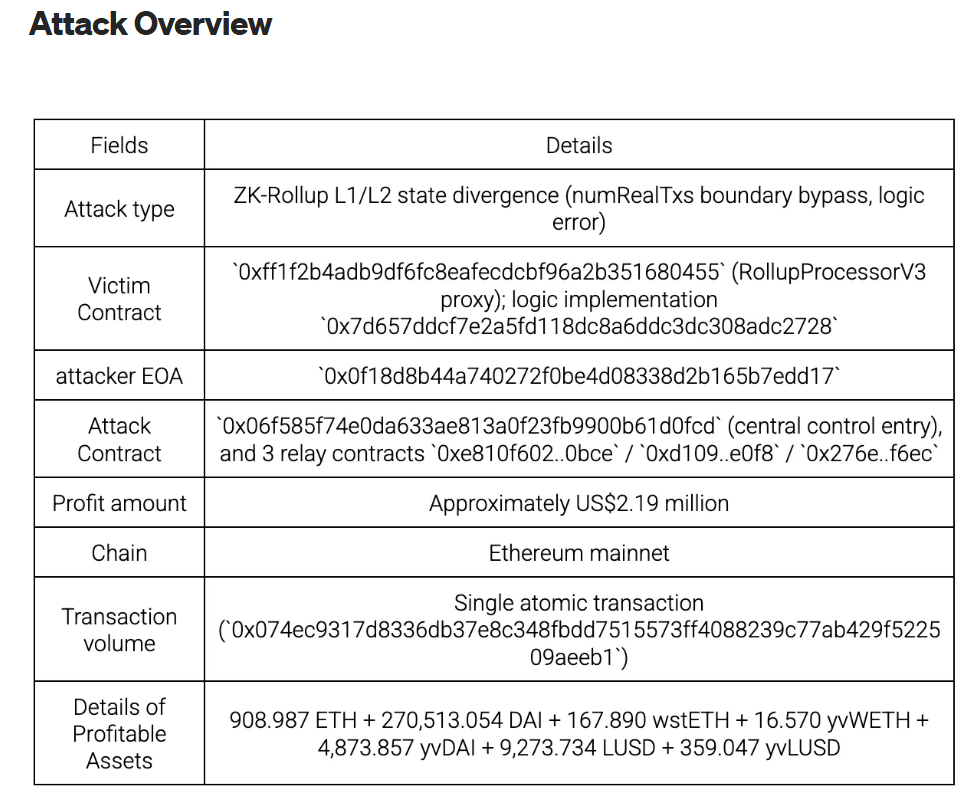
First Aztec exploit, attack overview. Source: SlowMist
For protocols with deprecated smart contracts that still hold legacy assets, SlowMist advised an orderly asset migration to eliminate the risks of ongoing cybersecurity exposure.
Magazine: The legal battle over who can claim DeFi’s stolen millions