The Checklist Delusion at the Heart of the Control
Why a Complete File Is Not a Working Control
Most financial institutions still treat customer due diligence (CDD) as a file to be completed rather than a control to be operated. The moment the file is signed off, the customer moves into the book, and the customer risk profile quietly freezes. A complete
customer due diligence file is not a working control.
Done right, the mechanism is engineered as a control plane that orchestrates evidence, decisions, and accountability across the customer lifecycle. Run as a checklist, the risk profile goes stale, the high risk cases surface too late, and the audit trail
collapses on contact with a supervisor.
What the Standard Actually Requires
FATF Recommendation 10 Frames Four Continuous Obligations
Every serious standard already describes customer due diligence (CDD) as continuous and risk-calibrated. FATF Recommendation 10 requires financial institutions to identify the customer, verify identity from reliable independent sources, understand the purpose
of the business relationship, and conduct ongoing monitoring across the life of that relationship (1).
UK Money Laundering Regulations, Regulation 28
Regulation 28 of the Money Laundering Regulations 2017 is the operative rule in the UK: identify and verify customers, take reasonable measures to verify beneficial owners, and assess the purpose and intended nature of the business relationship (3). The
rule anchors that satisfaction in identity verification from an independent source, and the decision has to be made again every time the underlying facts move.
Ongoing Monitoring Is a Statutory Duty, Not a Best Practice
The same regulation, at subsection 28(11), defines ongoing monitoring as the part of customer due diligence that runs continuously — scrutiny of the customer’s activities across the relationship and keeping the underlying records up to date (4). For the
operational evidence behind that argument — [why periodic review fails operationally as ongoing monitoring](https://www.finextra.com/blogposting/31323/event-driven-kyc-refresh-why-periodic-review-fails-operationally)
— the case is already made in detail.
EU AML Regulation and the End of Transposition Gaps
Article 20 of Regulation (EU) 2024/1624 makes the same components directly applicable across every Member State from 10 July 2027, closing the national transposition gaps the old directive left behind (5). Article 26 elevates ongoing monitoring to a relationship-level
duty and requires obliged entities to keep the documents, data and information up to date as part of that duty (6).
FinCEN’s Four Core Elements
Under the US anti money laundering regime, 31 CFR 1010.230 and the 2016 CDD Final Rule preamble set out four core elements of customer due diligence: customer identification and verification, beneficial ownership identification and verification, understanding
the nature and purpose of the relationship to develop a customer risk profile, and ongoing monitoring with risk-based updates to customer information (7).
Why the Checklist Model Breaks Under Real Customer Risk
The Risk-Based Approach Is Incompatible With Uniform Checks
FATF Recommendation 1 requires measures commensurate with assessed money laundering and terrorist financing risk — enhanced where risk is higher, simplified where lower-risk conditions are demonstrably met (2). A uniform checklist is non-compliant by design,
because it applies the same measures to every potential customer regardless of what the risk assessment requires. A control plane calibrates; it mitigates risks where they concentrate.
Static Files Cannot Track Risk Profiles That Move
Financial institutions operating at any scale watch the customer risk profile change in ways the onboarding file will never see: new counterparties, new jurisdictions, adverse media on a beneficial owner, politically exposed persons status acquired mid-relationship.
A file captured at onboarding is a photograph of a moment. Customer risk management is a live variable, and customer due diligence captured once at onboarding cannot represent the customer the firm is actually serving a year later.
Escalation Triggers Do Not Fire Themselves
Enhanced due diligence is only effective when the trigger fires the moment the facts change: a new high risk third country exposure, a beneficial owner flagged on a sanctions list, high risk counterparties surfacing mid-relationship, a pattern in the customer’s
activities that does not match the declared business. A checklist has no trigger. A control plane does, and the financial crime exposure in a high risk segment is where the difference shows up first.
The Control Plane Mechanism in Four Jobs
Evidence Capture as a Continuous Input Layer
The first job is to capture evidence continuously from reliable, independent sources. Verification of the customer’s identity is the starting point, not the endpoint. Beneficial ownership data, transaction patterns, counterparty exposure, sanctions screening
and adverse media feeds all flow into the same evidence layer. Under this model the customer due diligence (CDD) process becomes an input pipeline rather than a filing cabinet. For a potential customer at onboarding the pipeline captures the initial file,
and the FinCEN CDD Final Rule explicitly requires covered financial institutions to keep customer information current on a risk basis.
Risk Scoring and Event-Driven Monitoring as the Decision Layer
The second job is to score every potential customer — turning that evidence into a customer risk score that actually drives decisions, and firing the monitoring events that keep the score current. In a checklist model the risk level is typically a categorical
field completed at onboarding; in the decision layer the score is a continuously recalculated output of live customer due diligence. EBA/GL/2023/03 pushes financial institutions in the same direction (14). Event-driven triggers sit on top of the score. Threshold
breaches, counterparty changes, geography shifts, politically exposed persons alerts, beneficial ownership changes — each fires a calibrated action against the relevant customer file, and each surfaces suspicious transactions before they accumulate.
Accountability as the Named Decision Layer
The third job is the one checklists never had: every material decision has to attach to a named human with authority. FATF Recommendation 18 and the Basel Committee’s sound management guidance both anchor the aml compliance programme to a senior officer
whose concerns must be heard at board level (8). In the UK that officer is the Money Laundering Reporting Officer at SMF17 under the FCA’s Senior Managers Regime, with a personal duty of responsibility for failings in their area (9). This is the discipline
[the control plane analogy applied to KYC infrastructure more broadly](https://www.finextra.com/blogposting/31285/control-plane-thinking-treat-kyc-like-payments-infrastructure-not-a-one-off-check)
is really describing: the decision record has to be legible to the named officer who is liable for it.
What the FCA Saw When the Control Ran as a Checklist
Nationwide: Five Years of a Frozen File
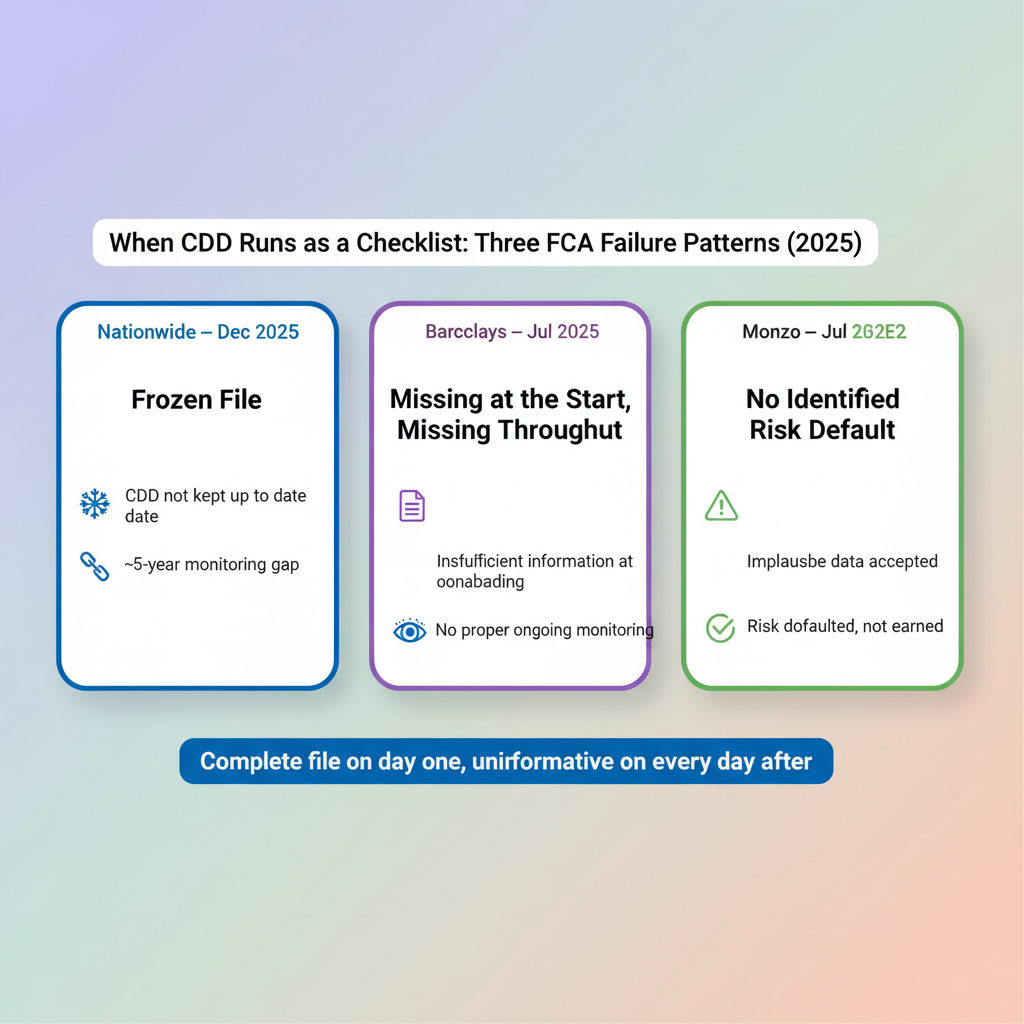
When the FCA fined Nationwide Building Society £44 million in December 2025 for failings in financial crime controls, the operative finding was that the firm had ineffective systems for keeping customer due diligence (CDD) up to date and for monitoring transactions
across a nearly five-year window, leaving it unable to identify, assess, monitor or manage the money laundering risks across its personal current account base (10) — existing customers onboarded and then effectively frozen while the financial crime risk in
their accounts moved on without them. The customer due diligence file was complete on day one and uninformative on every day after.
Barclays: Missing at the Start, Missing Throughout
The pattern repeats in the July 2025 Barclays action on the poor handling of financial crime risks. In the Stunt & Co matter the FCA’s operative finding was verbatim and short: Barclays “did not gather enough information at the start of the relationship
or carry out proper ongoing monitoring” (11). In just over a year, £46.8 million from a known money laundering operation moved through one customer relationship. Read against the Regulation 28 obligation — know the purpose and intended nature of the business
relationship, monitor continuously — the supervisory language names the customer due diligence lifecycle gap directly.
Monzo: The “No Identified Risk” Default
The July 2025 Monzo Final Notice completes the set. The FCA found a risk assessment framework that defaulted most personal customers to “no identified risk” and an onboarding default that accepted obviously implausible information — customers using famous
London landmarks as their residential address (12). The failure was not in the diligence of the compliance team but in the absence of a mechanism that forced the risk assessment of a potential customer to be earned rather than defaulted, leaving the whole
base of high risk customers statistically invisible to the people responsible for managing them.
Beneficial Ownership and the Adequate, Accurate, Up-to-Date Standard
Why a One-Time Beneficial Owner File Cannot Meet the Standard
FATF tightened Recommendation 24 in March 2022 to require that beneficial ownership information on legal persons be adequate, accurate and up-to-date (13). A file captured at onboarding and never refreshed cannot meet any of those three tests after the first
ownership change, corporate restructuring, or nominee substitution. It is the hardest test of a control plane — identifying the owner once is the easy part, and keeping those checks current on the people behind the legal person is the part financial institutions
systematically underestimate.
Calibrating the Control Across the Risk Spectrum
Simplified, Standard and Enhanced as Bands Inside One Control Plane
Simplified due diligence is not a shortcut. It applies only where lower-risk conditions are demonstrably met, and the burden of proof sits with the firm: positive evidence is the burden, not the absence of negative evidence, and low risk customers have to
remain an output of the risk assessment rather than an input that bypasses it.
The escalation path is not a separate workflow. Politically exposed persons, high risk third country exposure, unusual transaction patterns tied to terrorism financing risks, adverse media on a beneficial owner — each triggers a calibrated intensification
of the standard customer due diligence process inside the same mechanism, not a parallel regime bolted on at the side.
What the Control Plane Gives the Firm That the Checklist Cannot
A Defensible Answer to the Question Regulators Actually Ask
The question a supervisor asks on an examination visit is not “do you have a customer due diligence policy?” It is “show me how you knew this customer’s risk profile was accurate on 12 March, and show me who decided that.” A control plane answers that question
on demand, at the level of an individual decision, with the evidence, the risk score, the trigger history and the named decision owner attached. A checklist answers with a file.
The three financial institutions the FCA cited in 2025 did not fail because their compliance teams were careless or their aml compliance budgets were thin. They failed because the mechanism ran as a form rather than as a live control, and when the customer
relationships moved, the files did not move with them. Those are the regulatory requirements the three firms missed, and the financial crime exposure that followed was structural rather than accidental. A complete file will never beat a live mechanism when
the regulator walks in.
*By Victor Mendez, Co-Founder & CMO, Verifyo*
Sources
(1) Financial Action Task Force. International Standards on Combating Money Laundering and the Financing of Terrorism & Proliferation — The FATF Recommendations, Recommendation 10. October 2025.
https://www.fatf-gafi.org/en/publications/Fatfrecommendations/Fatf-recommendations.html
(2) Financial Action Task Force. FATF Recommendations — Recommendation 1: Assessing risks and applying a risk-based approach. October 2025.
https://www.fatf-gafi.org/en/publications/Fatfrecommendations/Fatf-recommendations.html
(3) HM Government. The Money Laundering, Terrorist Financing and Transfer of Funds (Information on the Payer) Regulations 2017, SI 2017/692, Regulation 28. 2017.
https://www.legislation.gov.uk/uksi/2017/692/regulation/28
(4) HM Government. The Money Laundering, Terrorist Financing and Transfer of Funds (Information on the Payer) Regulations 2017, SI 2017/692, Regulation 28(11). 2017.
https://www.legislation.gov.uk/uksi/2017/692/regulation/28
(5) European Parliament and Council. Regulation (EU) 2024/1624 on the prevention of the use of the financial system for the purposes of money laundering or terrorist financing, Article 20. 31 May 2024.
https://eur-lex.europa.eu/eli/reg/2024/1624/oj/eng
(6) European Parliament and Council. Regulation (EU) 2024/1624, Article 26 — Ongoing monitoring of the business relationship. 31 May 2024.
https://eur-lex.europa.eu/eli/reg/2024/1624/oj/eng
(7) Financial Crimes Enforcement Network. 31 CFR 1010.230 — Beneficial ownership requirements for legal entity customers. 11 May 2018.
https://www.law.cornell.edu/cfr/text/31/1010.230
(8) Basel Committee on Banking Supervision. Sound management of risks related to money laundering and financing of terrorism.
https://www.bis.org/bcbs/publ/d505.htm
(9) Financial Conduct Authority. Senior Managers Regime — SMF17 and duty of responsibility.
https://www.fca.org.uk/firms/senior-managers-and-certification-regime/senior-managers-regime
(10) Financial Conduct Authority. FCA fines Nationwide £44m for failings in financial crime controls. 12 December 2025.
https://www.fca.org.uk/news/press-releases/fca-fines-nationwide-44m-failings-financial-crime-controls
(11) Financial Conduct Authority. FCA fines Barclays £42 million for poor handling of financial crime risks. 16 July 2025.
https://www.fca.org.uk/news/press-releases/fca-fines-barclays-42-million-poor-handling-financial-crime-risks
(12) Financial Conduct Authority. FCA fines Monzo £21m for failings in financial crime controls. 7 July 2025.
https://www.fca.org.uk/news/press-releases/fca-fines-monzo-21m-failings-financial-crime-controls
(13) Financial Action Task Force. Recommendation 24 (Transparency and beneficial ownership of legal persons). March 2022.
https://www.fatf-gafi.org/en/topics/beneficial-ownership.html
(14) European Banking Authority. Guidelines amending the ML/TF Risk Factors Guidelines (EBA/GL/2023/03). 3 November 2023.
https://www.eba.europa.eu/sites/default/files/document_library/Publications/Guidelines/2023/1054143/Amending%20GLs%20to%20the%20RFGLs%20in%20relation%20to%20NPOs.pdf